
Security testing does not end when the report is delivered.
Most security consultancies deliver a PDF and move on. Pentrox gives you a secure client platform where findings, retests, and reports are visible in real time, from the first day of the project through to completion.
Real-time visibility. Structured retests. Reports on demand. Part of every assessment.
What gets lost between the last test day and the final PDF
Testing finishes on a Friday. The report arrives weeks later in an email thread nobody can find when it matters.
By then, critical issues have sat unreported for days, retesting has become a separate conversation, and the original findings no longer reflect what has been fixed.
Transparency should not depend on how often somebody chases an email.
A working space for the entire assessment
portal.pentrox.nl
The Pentrox Portal is the secure environment where findings, reports, and retests are managed from project start through retest completion.


What the Pentrox Portal does for you
Six capabilities form the core of the Pentrox Portal. Each one removes a specific point of friction from the traditional penetration testing delivery model.
Findings Dashboard
See findings as they are discovered, not weeks later.
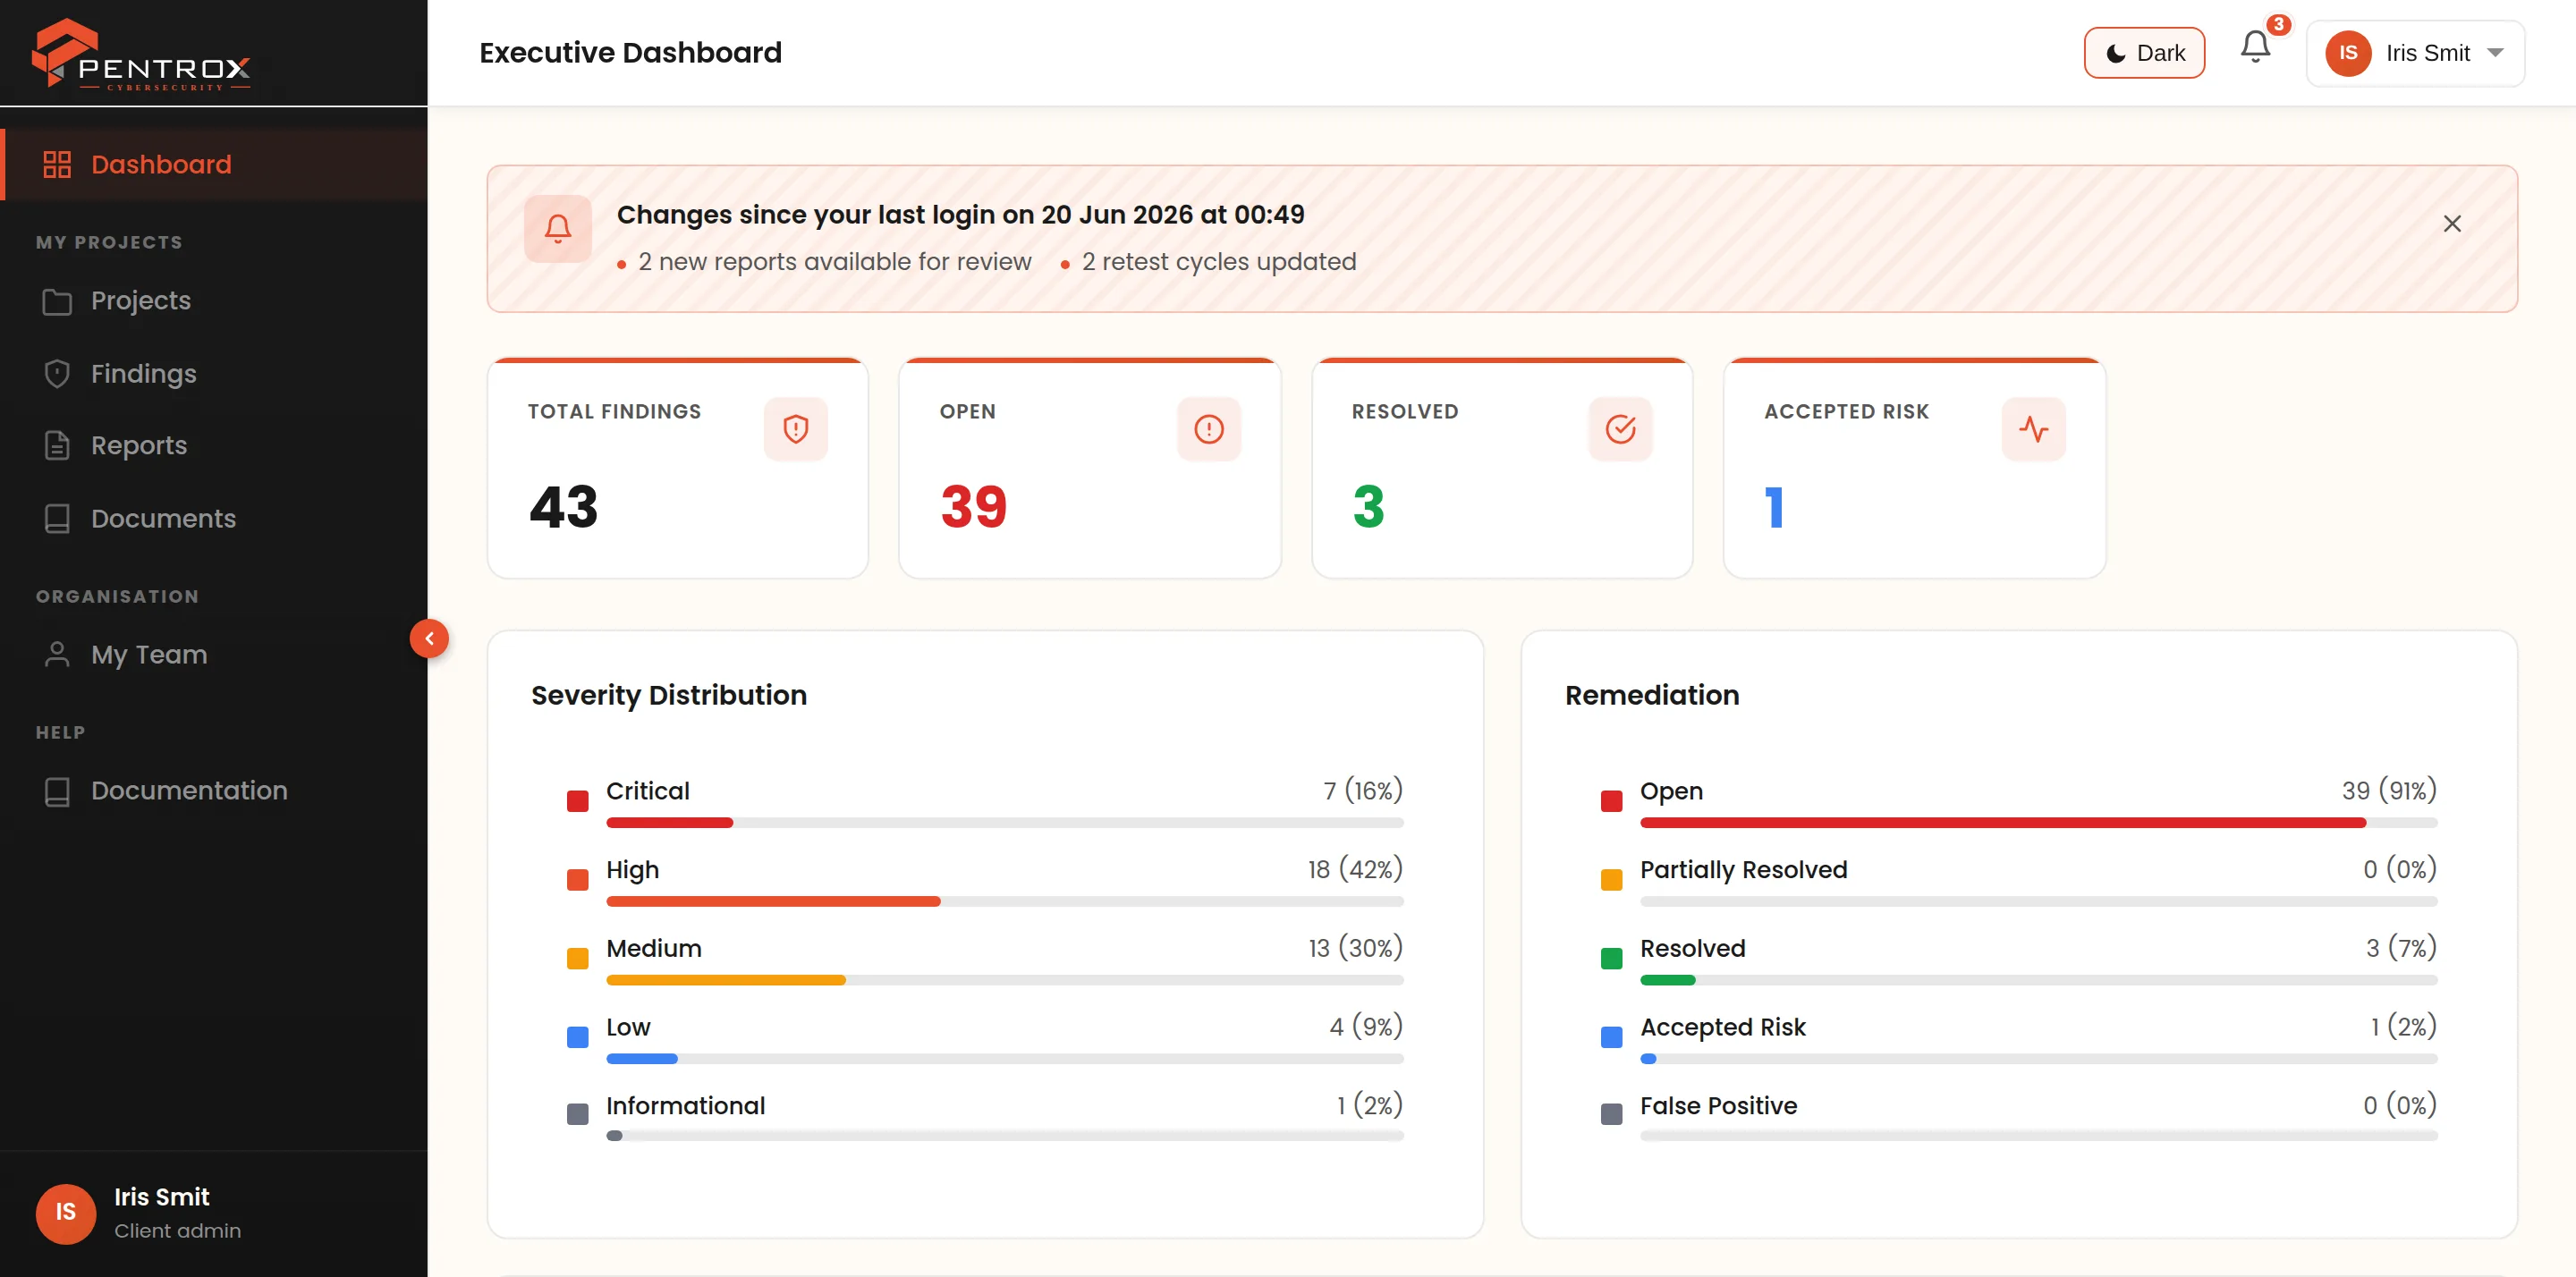
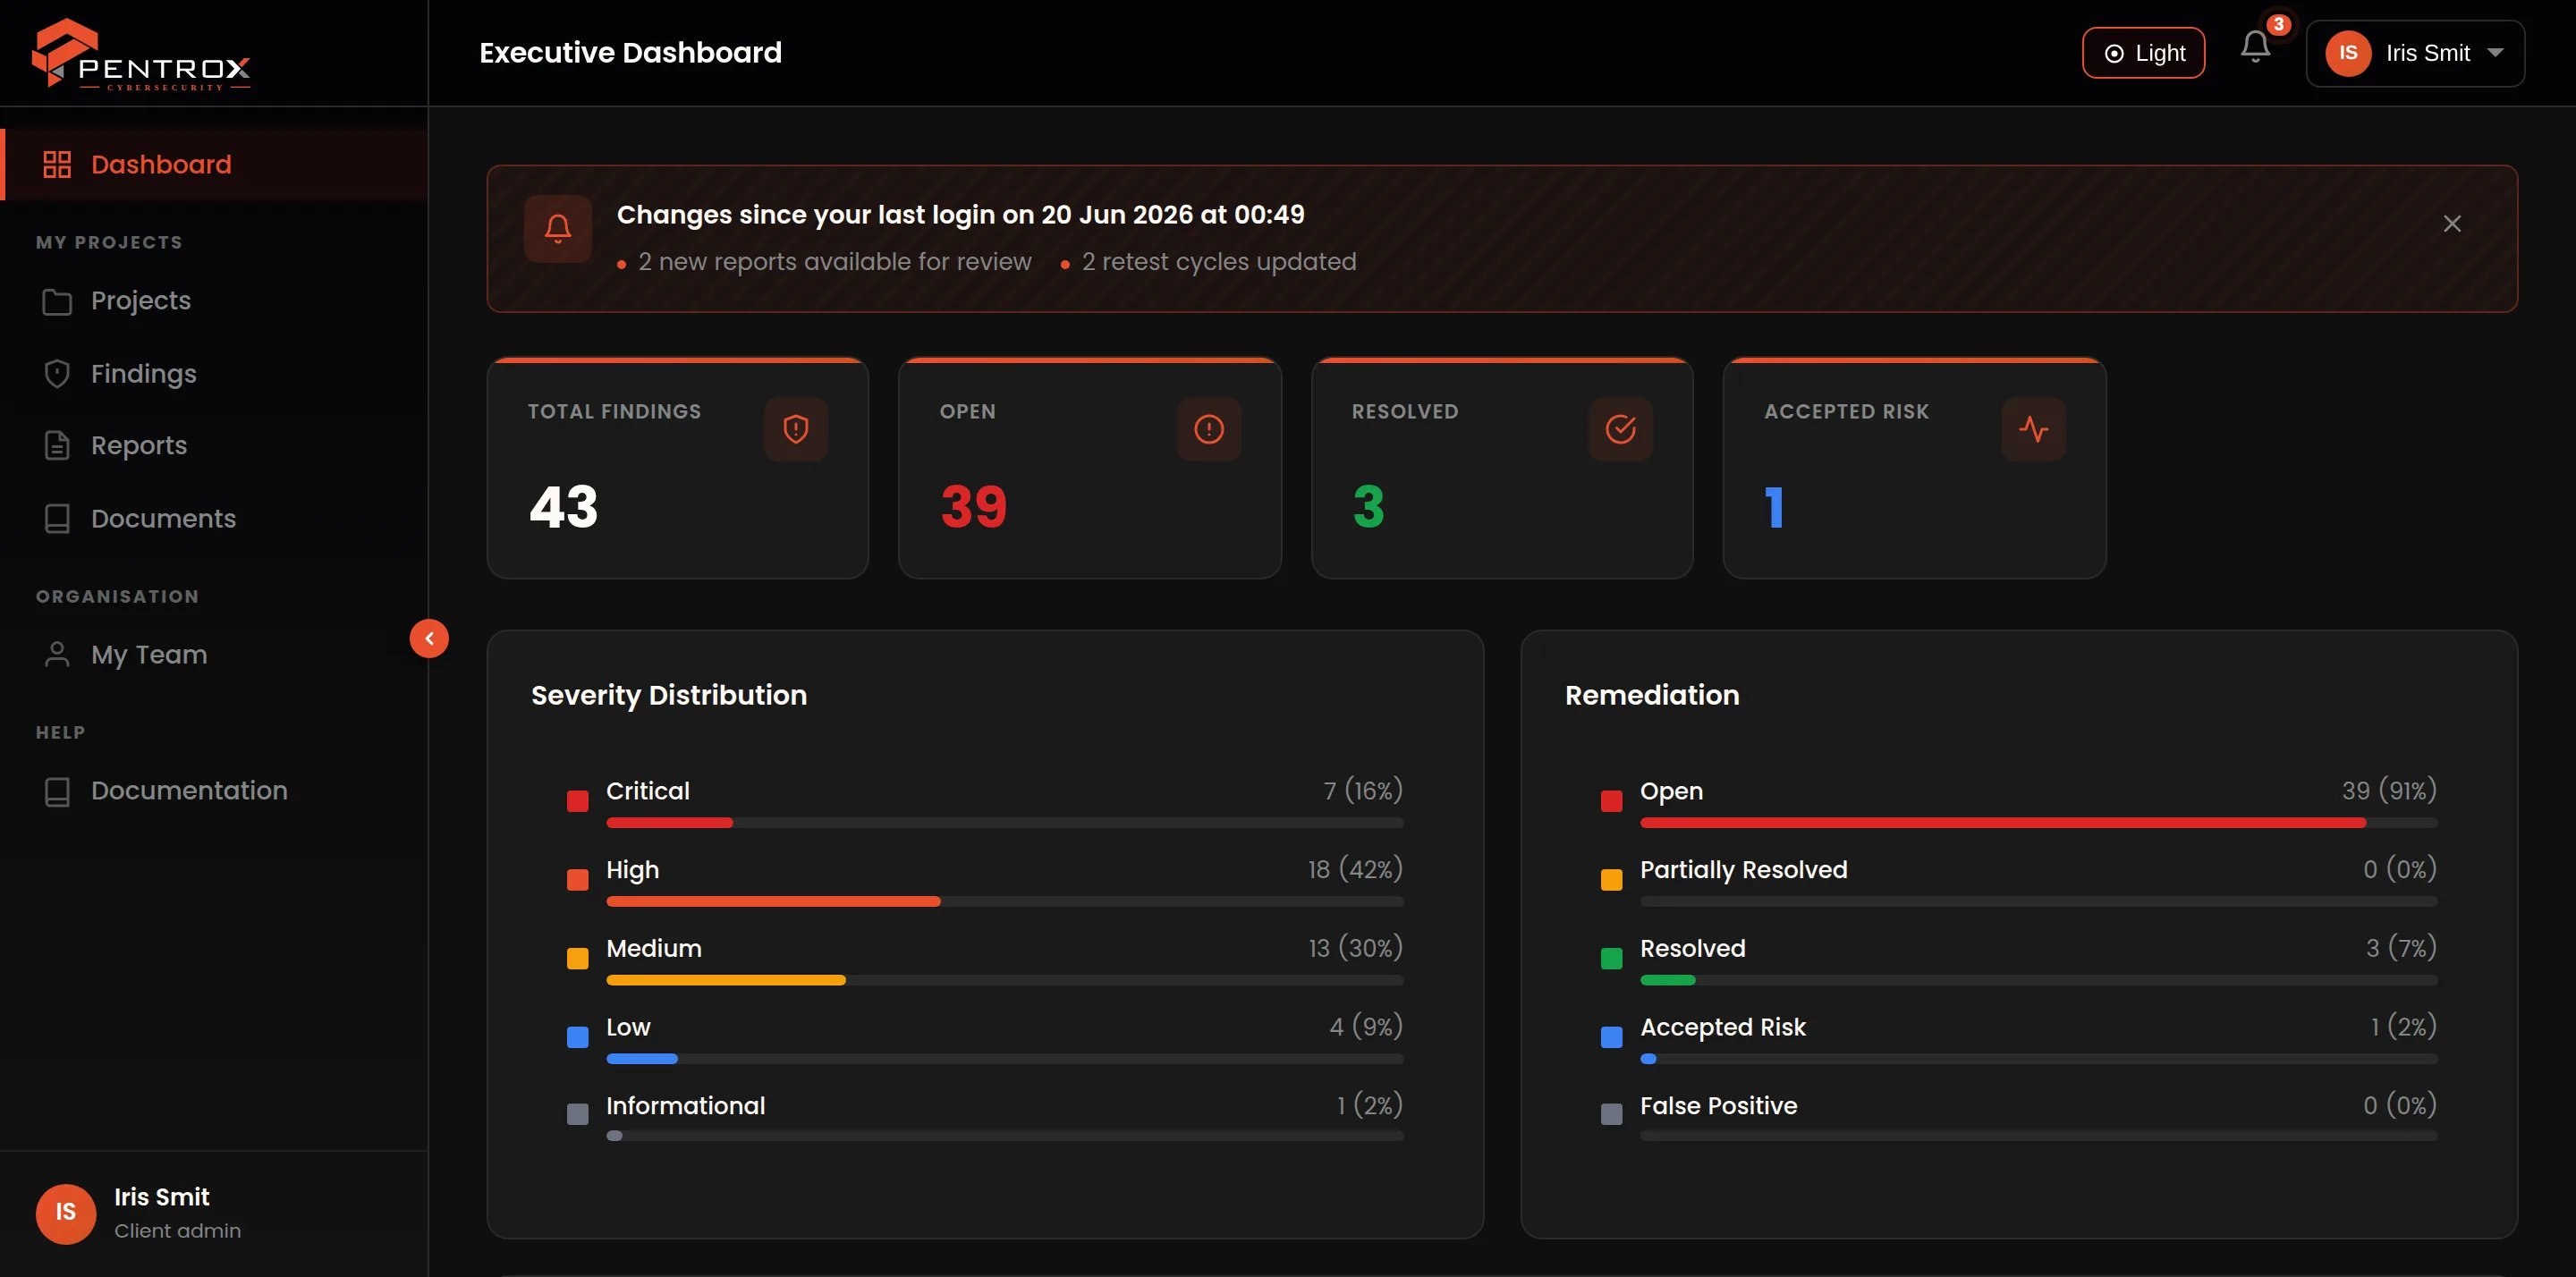
Every finding across every active project is visible from the moment you sign in. Summary statistics, severity breakdowns, and trend data give you an immediate understanding of where you stand and how your posture is changing over time.
- Severity breakdown by project
- Monthly trend analysis
- Recent findings with full context
Multi-cycle Retests
Retests managed in the portal, no additional cost.
Flag remediated findings for retest, submit the request, and receive individually verified results per finding. If issues remain after the first cycle, request a second or third. Retesting is included with every assessment at no additional cost.
- Per-finding verification results
- Multiple retest cycles included
- Automated status notifications
Report Library
Four report types, published and ready to download.
All reports are published to a centralised library and available for immediate download. Four report types are supported: Initial, Management, Retest, and Retest Management. Historical reports remain accessible at any time.
- Four dedicated report types
- Immediate download on publication
- Full historical access retained
Project Lifecycle
Six stages, from scheduled to completed.
Every project moves through six visible stages, from Pending to Completed. The current stage updates in real time and notifications are sent automatically when the status changes, a report is published, or new findings become available.
- Six clearly defined stages
- Real-time status updates
- Automatic change notifications
Documents & Requirements
Everything you need to provide, in one place.
Before testing begins, Pentrox shares a Required Item List outlining what is needed for the assessment. You provide access details, credentials, URLs, source code, and technical documentation directly through the portal. All files are exchanged within a secure project environment, not through email.
- Clear list of required items per project
- Secure upload of credentials and documentation
- All exchanges within the portal, not email
Team & Access
Decide who sees which project.
Client administrators manage their own team members, assign them to specific projects, and adjust access as the organisation evolves. Every user is required to enrol in two-factor authentication before the first sign-in.
- Role-based project access
- Mandatory two-factor authentication
- Client-managed team membership
Project Conversation
Talk to the testing team directly, no account managers in between.
Each assessment has a single conversation thread shared between your team and the testers. Ask a question, reply, mention a colleague, attach a file, or point to a specific finding, all in the same place the work happens. The context stays with the assessment instead of scattered across separate email threads.


The difference in delivery.
The traditional model treats the report as the deliverable. The Pentrox Portal treats the assessment as a shared working environment from the first day until every finding is closed.
| Traditional pentest delivery | With the Pentrox Portal |
|---|---|
| Final PDF arrives weeks after testing ends. | Findings become visible as they are published during the assessment. |
| Critical issues discovered mid-test wait for the report. | Critical findings are communicated immediately. |
| Retest is a separate quote, a separate email thread, or not offered. | Retests are managed in the Pentrox Portal at no additional cost. |
| Multiple retest rounds are unusual or billed per cycle. | Multi-cycle retests are supported until all findings are addressed. |
| Reports are attached to emails and lost over time. | Every report is always available in the centralised library. |
| Project status requires a phone call or an email. | Project status is visible in real time with automatic notifications. |
| Scope documents and evidence are exchanged over email. | Documents are uploaded and downloaded through a secure channel. |
| Access to findings is all-or-nothing. | Role-based access ensures each user sees only what they should. |
Before and after the Pentrox Portal
Built by people who break into portals for a living.
The same standards Pentrox audits in client systems are applied to the Pentrox Portal itself. Client platforms are a recurring target in the assessments we perform. That perspective shapes how the portal is built and maintained.
Mandatory two-factor authentication
Every user, including every client user, must enrol in two-factor authentication before the first sign-in. No exceptions, no fallback to password-only access. A passkey (FIDO2) can be used as the second factor in place of the authenticator app.
Strict access isolation
Access to project data is enforced at the application level. Every request is authenticated and authorisation-checked so users see only their own projects. Access control logic has been tested against common bypass techniques including IDOR and privilege escalation.
Tested by the same team
The portal undergoes the same type of security assessment that Pentrox performs for clients. Vulnerabilities are identified, remediated, and verified before they reach production.
No hidden charges, no quiet limits.
Every point below applies to every assessment, regardless of scope or budget.
No per-user licensing
Every team member receives portal access. There is no cap on users and no additional fee per seat.
No expiry on access
Your project data, findings, and reports remain available in the portal after the assessment is complete. Project data is removed when you request it.
Senior-led, peer-reviewed
Every assessment is performed or supervised by senior ethical hackers. An internal quality review is completed before publication.
Start your next assessment with full visibility from day one.
Every Pentrox assessment includes access to the Pentrox Portal, retesting, and senior-led testing as standard. Request a quotation and receive access to the Pentrox Portal the moment the project is confirmed.
Request a quotationResponse within one business day.